Adding AI to an established product rarely requires a ground-up rebuild. The safer route is usually to choose one valuable workflow, place the AI capability behind a controlled interface, measure its behaviour, and expand only when the evidence supports doing so.
That matters because AI adoption is growing, but adoption is not the same as deep integration. The Office for National Statistics reported in July 2026 that self-reported AI use among UK businesses with 10 or more employees had risen from around 12% in late 2023 to around 35% in June 2026, while the average number of AI technologies used by adopting businesses rose only modestly. Its September 2026 survey later recorded 38% usage for businesses with 10 or more employees. Different surveys use different definitions and populations, so these figures should not be treated as interchangeable; together, they show rising interest and uneven maturity (ONS analysis, ONS October 2026 bulletin).
For an existing software product, the useful question is not “Where can we put AI?” It is:
Which painful user workflow could improve measurably if the product handled one uncertain, repetitive or language-heavy step better?
The workflow comes before the model. That principle keeps the project tied to user value and gives the team a way to evaluate whether AI deserves a permanent place in the product.
Start with a narrow workflow, not an AI roadmap
A broad ambition such as “add an assistant” is difficult to design, test or govern. A bounded workflow is easier to reason about. Examples might include:
- classifying an incoming request before a person reviews it;
- drafting a summary from information the user has already supplied;
- suggesting relevant knowledge-base material;
- extracting defined fields from a document for confirmation;
- producing a first draft that a qualified employee must approve; or
- highlighting anomalies for investigation without making the final decision.
The strongest starting point has five characteristics:
- The current problem is visible. The team can describe where time, errors or user frustration occur today.
- The output can be checked. A person, rule or trusted dataset can determine whether the result is useful.
- A mistake is recoverable. The first release does not put safety, rights, money or irreversible actions entirely in the model’s hands.
- The data boundary is understandable. The team knows what information is needed, where it comes from and whether it can be sent to the chosen service.
- Success has a measurable outcome. The team can compare the AI-assisted workflow with the existing process.
This approach also answers a common architectural concern: the existing product can remain the system of record. AI becomes one service used for a specific task, not a replacement for authentication, business rules, databases, payments or every existing screen.
Define the outcome before choosing a model
Model comparisons are tempting because they feel concrete. They are still premature until the team defines what “good” means for the workflow.
For a support-summary feature, success might include:
- the summary includes every critical fact from the source material;
- it does not introduce unsupported claims;
- a reviewer can correct it quickly;
- the response arrives within an acceptable time;
- the cost per completed workflow remains affordable; and
- users can continue without the feature when it is unavailable.
For document classification, quality might be measured using a reviewed test set, false-positive and false-negative rates, escalation frequency, and time saved after human review. For a drafting feature, the better metric may be acceptance with edits rather than raw generation volume.
Avoid using a single “accuracy” number without defining how it was produced. Different errors have different consequences. Missing a harmless optional label is not equivalent to placing a sensitive request in the wrong queue. Evaluation should reflect the product’s actual risk.
Audit the data path before connecting an AI service
An AI feature creates a new data flow. Before building it, map:
- what the user submits;
- what the existing product retrieves;
- what is sent to the model provider;
- what the provider retains or logs;
- where prompts, outputs and feedback are stored;
- who can view those records;
- whether subprocessors or international transfers are involved; and
- how information is deleted or corrected.
Use the minimum data required for the task. Remove identifiers where they are not necessary. Do not treat a prompt box as a harmless text field: users may paste confidential, personal or commercially sensitive material into it.
The Information Commissioner’s Office provides an AI and data protection risk toolkit to help organisations assess risks to people’s rights and freedoms. The ICO notes that this guidance is under review following the Data (Use and Access) Act, so teams should check its current status rather than relying on a saved interpretation indefinitely.
If personal data is involved, bring the organisation’s privacy lead or qualified adviser into the workflow design early. Clarify the purpose and lawful basis, transparency information, retention, individual rights, security and whether a data protection impact assessment is required. This article is product-engineering guidance, not legal advice.
Put AI behind a stable product boundary
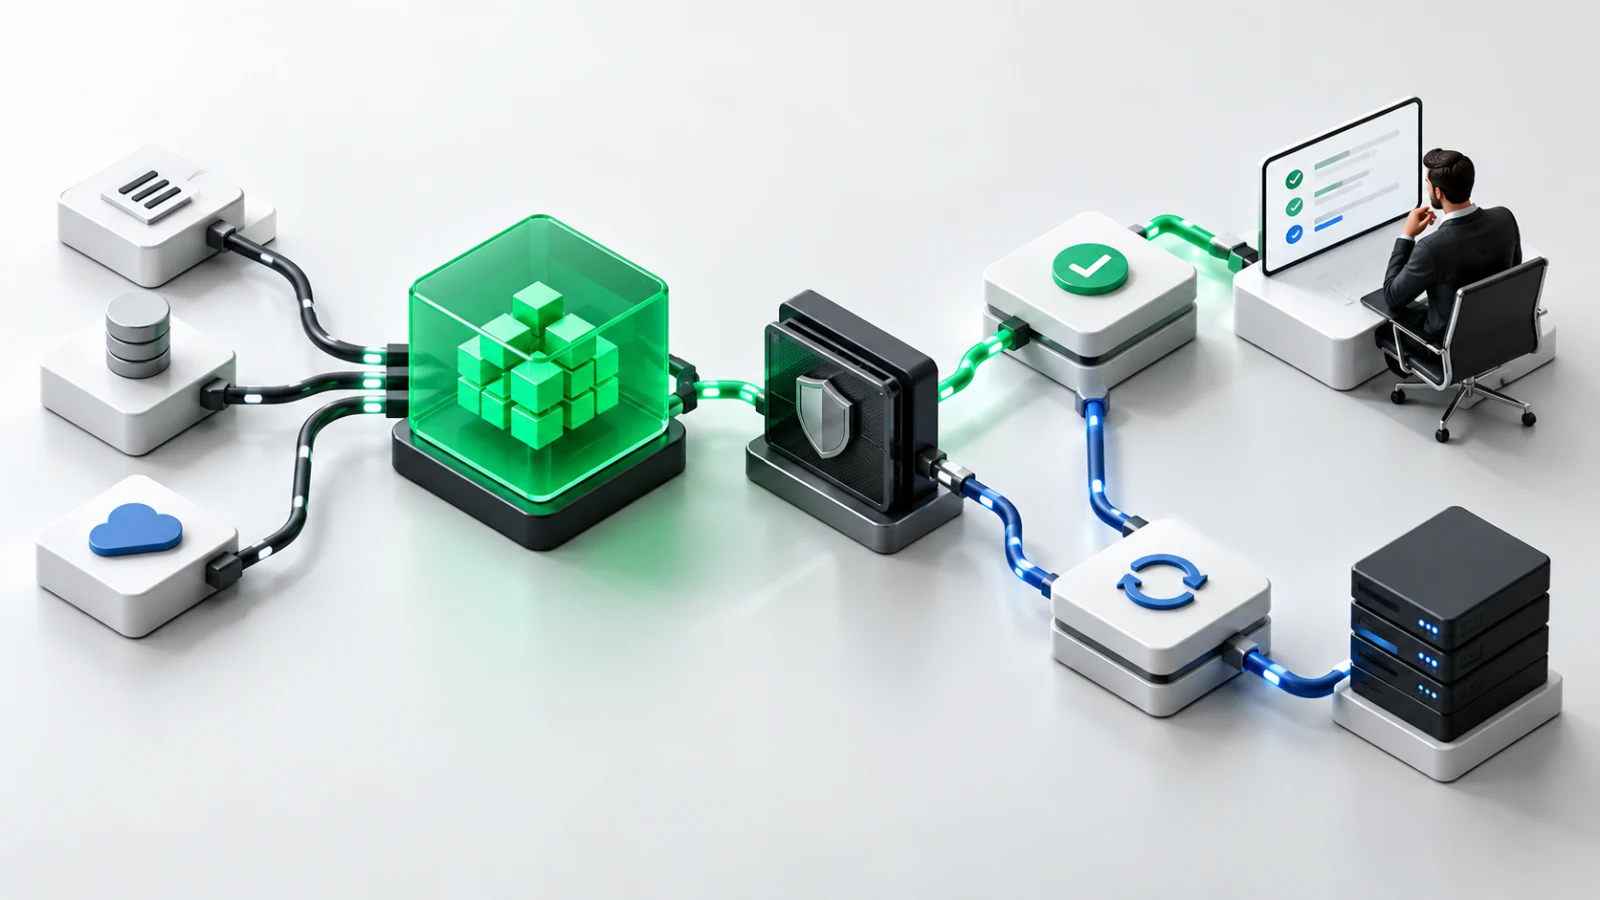
The most maintainable integration treats the model as a replaceable dependency. The user interface and core business logic should call an application-owned service rather than allowing every screen to communicate directly with a model provider.
A practical boundary can:
- assemble approved context;
- remove or mask unnecessary data;
- apply a versioned prompt or instruction;
- select the appropriate model and settings;
- validate the response shape;
- enforce permissions and action limits;
- record safe operational telemetry;
- route failures to a fallback; and
- support changing providers without rewriting the whole product.
This is an architectural seam. On one side sits the product’s trusted state, permissions and deterministic rules. On the other sits a probabilistic capability that may return a poor answer, time out, change across model versions or become unavailable.
The UK National Cyber Security Centre’s guidelines for secure AI system development apply to systems built on external models and APIs as well as models developed from scratch. They cover secure design, development, deployment, operation and maintenance. The NCSC’s secure-design guidance also recommends controlling what data can leave the organisation, sanitising inputs and restricting actions an AI component is allowed to trigger (NCSC secure design).
The boundary should therefore enforce capabilities, not merely document good intentions. If the feature may create a refund request, for example, it should propose a structured request for validation rather than directly moving money. If it can search private records, it should inherit the signed-in user’s permissions rather than use one unrestricted service account.
Design human review, fallback and failure states
“Human in the loop” is useful only when the person has enough context, time and authority to identify a bad result. A review screen should make the source material available, distinguish generated content, show uncertainty where meaningful and make correction straightforward.
Decide which of these patterns fits the risk:
- AI suggests; a person decides. Suitable where judgement or accountability must remain human.
- AI acts within a narrow reversible limit. The system may complete a low-risk task and retain an audit trail or undo option.
- AI escalates uncertainty. Low-confidence or unusual cases move to a person or the existing manual process.
- AI is optional assistance. The user can ignore it and finish the workflow conventionally.
Then define failure behaviour. What happens when the model times out, the provider rejects the request, structured output is invalid, usage limits are reached or the answer fails validation? “Try again” is not always enough. A resilient feature may show the original workflow, save the user’s progress, queue a retry, use a simpler deterministic method or route the item for manual processing.
The product should not conceal these transitions. Users need an honest explanation of what happened and what they can do next.
Evaluate quality, cost, speed, privacy and misuse together
A proof of concept that produces impressive examples is not yet a product feature. Evaluation needs a representative set of cases, including ordinary inputs, difficult edge cases and deliberately hostile or misleading inputs where relevant.
Create a versioned evaluation set from material you are permitted to use. Define expected characteristics rather than forcing one exact answer when several answers could be acceptable. Review results consistently and record why an output passed or failed.
Assess at least six dimensions:
| Dimension | Useful questions |
|---|
| User value | Does this make the target task materially easier or better? |
| Quality | Which errors occur, how often, and how serious are they? |
| Latency | Is the response fast enough for the workflow? |
| Cost | What is the end-to-end cost per successful task at expected volume? |
| Privacy and security | Is data exposure proportionate and controlled? |
| Misuse and resilience | Can inputs manipulate the feature, exceed its authority or cause unsafe downstream action? |
Track the whole workflow, not just model calls. If reviewers spend longer correcting output than doing the task manually, the feature is not creating value. If a cheaper model causes more escalations, its apparent saving may disappear. If better context improves quality but exposes more data, that trade-off needs an explicit decision.
Do not use live customers as an unannounced experiment. Test internally, use appropriately governed data, and explain the feature clearly when real users become involved.
Pilot with a controlled cohort
The first production release should be deliberately small. A controlled pilot might be limited by:
- one user role;
- one workflow;
- one market or account group;
- a feature flag;
- a low-risk data class;
- capped volume; and
- named people responsible for monitoring and support.
Before launch, establish a baseline for the current process. Then compare completion time, correction rate, abandonment, escalation, user feedback, service cost and operational incidents. Keep qualitative review alongside the metrics: a superficially fast workflow can still reduce trust if users must verify every result.
Set stop conditions before the pilot begins. These might include a serious privacy or security event, an unacceptable category of error, costs exceeding the agreed threshold or the fallback becoming overloaded. A stop condition protects the team from interpreting every warning as a reason to continue “learning”.
The pilot should end with a decision:
- stop because the workflow is unsuitable;
- revise the experience, data or model and test again;
- retain the capability for the narrow cohort; or
- expand gradually with the same controls and monitoring.
Keep the integration replaceable and observable
Once a pilot succeeds, operational work begins. Model behaviour, provider terms, prices and product requirements can change. Treat prompts, evaluation sets and safety rules as versioned product assets. Monitor quality signals, failures, latency, cost, escalations and user corrections. Re-run the evaluation set before changing the model, core instruction or important data source.
Document:
- the feature’s intended and prohibited uses;
- its data sources and retention;
- model and prompt versions;
- permissions and action limits;
- evaluation method and last review;
- fallback and incident process;
- the owner who can pause the feature; and
- dependencies needed to replace or retire it.
This discipline prevents one experiment from becoming an opaque critical dependency.
A practical sequence for adding AI without rebuilding
Use this order:
- Map one painful workflow and its present baseline.
- Define the user outcome and unacceptable failures.
- Confirm the minimum necessary data and privacy boundary.
- Build an application-owned integration service.
- Keep permissions, business rules and irreversible actions outside the model.
- Add structured validation, human review and a non-AI fallback.
- Evaluate representative normal, edge and misuse cases.
- Pilot with a controlled cohort and explicit stop conditions.
- Compare real workflow value with quality, cost, speed and risk.
- Expand only when the evidence supports the next step.
The existing product remains the foundation. AI earns its place one workflow at a time.
If you are strengthening the wider product before introducing a new dependency, start with our guide to secure mobile app development. You can also explore FlutterCraft’s product engineering services or join the newsletter for practical product guidance.
Sources and further reading


 Moeen AhmadLead Software Engineer24 Oct 202610 min read41