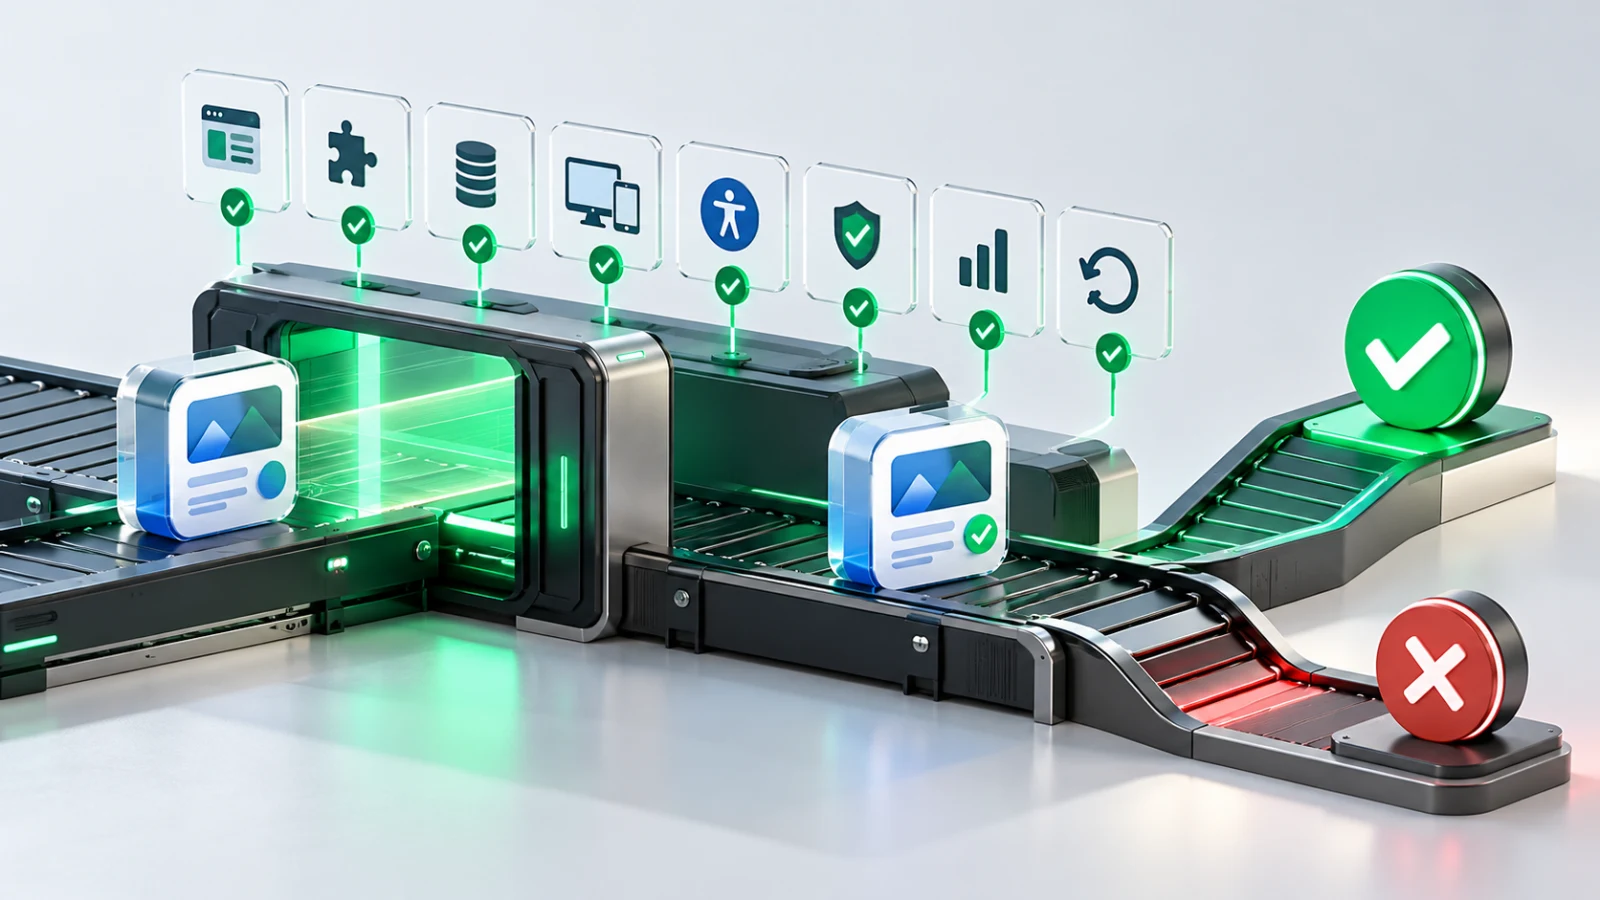
A startup does not need to test every possible combination before launch. It does need confidence that the journeys most important to users and the business will work, fail safely and be recoverable when something goes wrong.
Quality assurance is not a final hurdle owned by one tester. It is a shared discipline across product, design, engineering and operations.
A useful launch plan focuses on risk: what could fail, who would be harmed, how likely is it and how quickly can the team detect and recover from it?
Define quality through important outcomes
A product can have no obvious crashes and still be unready for launch.
For example, a user may be unable to complete sign-up, a payment may fail without a clear message, an account may show another user’s data, or support may have no way to understand what happened.
Start by identifying your critical journeys. These are the actions that must work for the product to deliver its first real value.
Typical critical journeys include:
- account creation and sign-in;
- onboarding;
- the main product action;
- payments or bookings;
- saving, editing or submitting important data;
- notifications or messages;
- account recovery;
- customer support;
- administrator actions.
For each journey, document the happy path, expected errors, edge cases and recovery route.
Use a launch-risk matrix
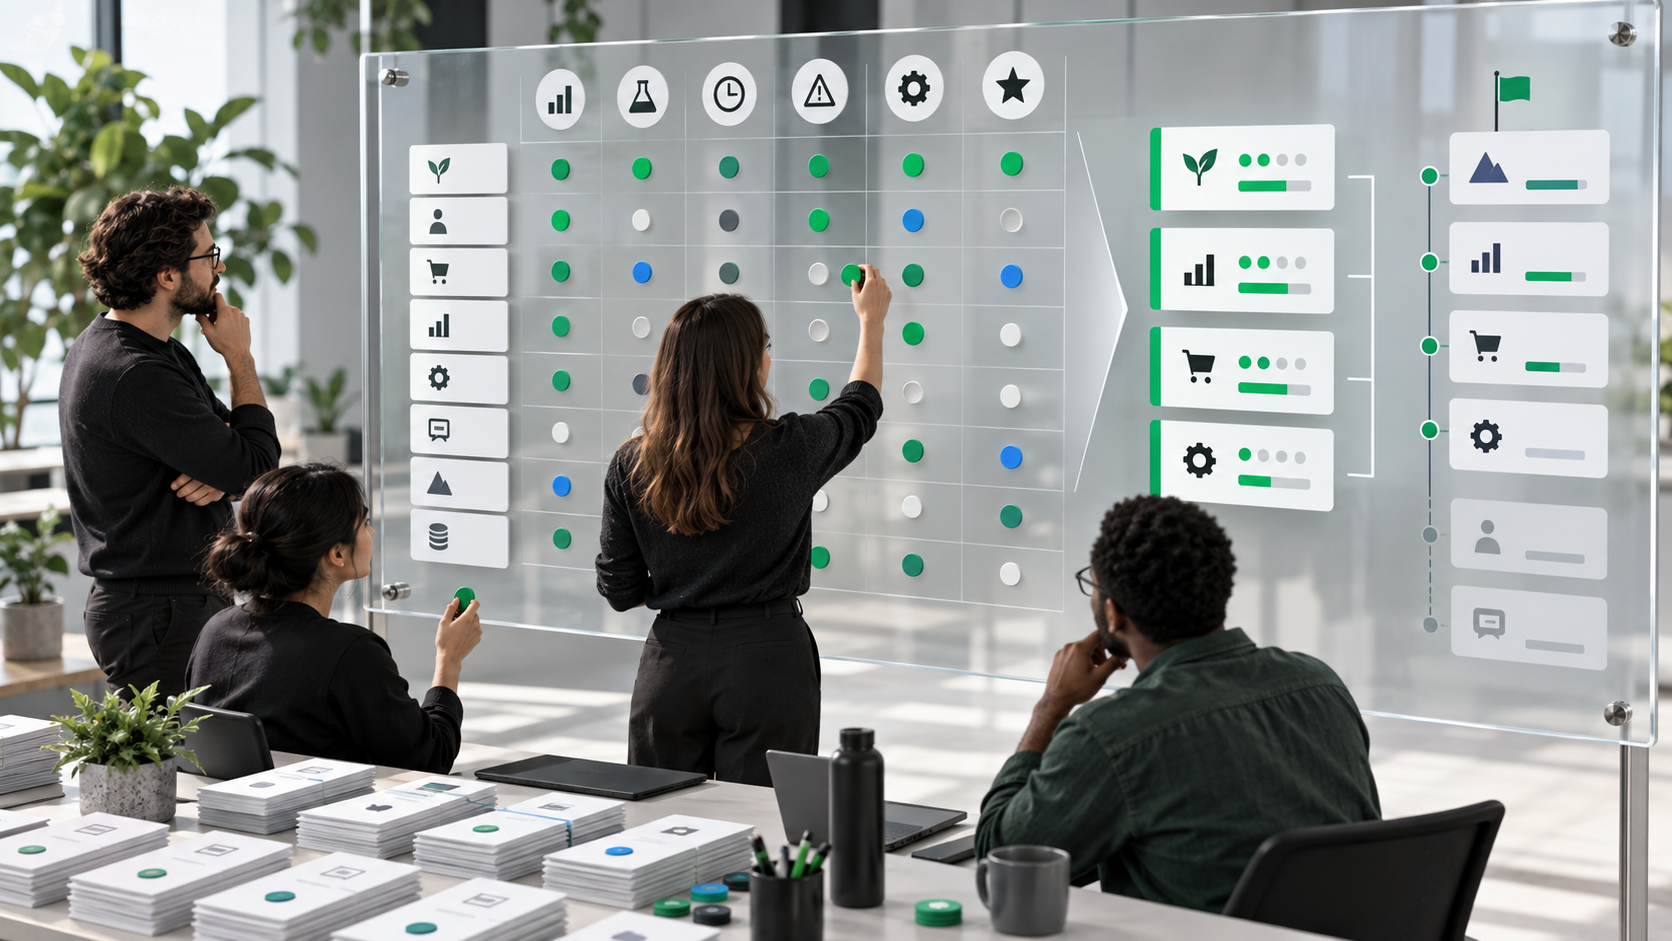
Score launch risks using impact and recoverability, not only probability.
| Risk area | Questions to ask |
|---|
| Critical journey | Can users complete the essential task from start to finish? |
| Data | Is information accurate, private, saved correctly and recoverable? |
| Integration | What happens if payment, identity, email or another dependency fails? |
| Device and network | Does the product behave acceptably on supported devices and weak connections? |
| Accessibility | Can users complete important tasks with relevant assistive technology and settings? |
| Security | Are access controls, secrets, validation and sensitive operations tested? |
| Analytics | Can the team see whether users reach first value and where they fail? |
| Release and rollback | Can the team detect a serious issue, pause harm and restore a safe state? |
High-impact, difficult-to-recover risks deserve attention before lower-impact visual polish.
Test the core journey and its failure states
For each critical journey, test more than the ideal flow.
Test:
- valid and invalid input;
- empty, loading and error states;
- expired sessions and account recovery;
- duplicate actions and repeated taps;
- interrupted networks;
- slow responses and timeouts;
- user cancellation and retry;
- incorrect permissions or roles;
- notification, email or integration failure;
- unsupported or unexpected data.
The goal is not to make errors invisible. It is to make errors understandable, safe and recoverable.
Test integrations as real systems
Third-party services often work perfectly in a development environment and fail under real conditions.
For every integration, confirm:
- credentials and environments are correct;
- live and test modes are not confused;
- webhook, callback or asynchronous events are handled safely;
- retries do not create duplicate records or duplicate charges;
- the product has useful error handling;
- ownership exists for monitoring and support;
- fallback behaviour is appropriate when the service is unavailable.
If a product relies on payments, identity verification, email delivery or external APIs, treat that dependency as part of the launch scope.
Test supported devices, browsers and networks
Your test matrix should reflect actual intended users, not every device ever made.
Define:
- supported operating-system versions;
- representative device sizes and performance levels;
- supported browsers for web journeys;
- slow, unstable and offline network conditions where relevant;
- orientation, text-size and language considerations where applicable.
Apple’s App Review Guidelines require apps to be complete, functional and tested for crashes and bugs before submission. They also require accurate metadata and accessible review access for account-based products. See Apple’s App Review Guidelines.
For Android, Google recommends combining manual accessibility testing, analysis tools, automated testing and user feedback. See Android accessibility testing guidance.
Include accessibility in launch QA
Accessibility is not a last-minute compliance exercise. It affects whether users can complete important tasks.
Test critical journeys with:
- larger text and display settings;
- keyboard navigation where relevant;
- screen readers such as VoiceOver or TalkBack;
- colour and contrast considerations;
- error messages and form labels;
- reduced-motion settings;
- touch targets and focus order.
Apple recommends testing apps with accessibility settings and assistive technologies such as VoiceOver, Voice Control and Switch Control. Apple accessibility testing guidance provides a practical approach.
WCAG 2.2 is an international accessibility standard covering websites, applications and other digital content. W3C WCAG guidance is a useful technical reference, but accessibility quality also benefits from direct user research and testing.
Check privacy and security alongside functionality
A feature is not ready simply because it produces the right screen.
Before launch, review:
- authentication and authorisation for each role;
- access to sensitive data;
- input validation and server-side business rules;
- secrets, API keys and production credentials;
- dependency and SDK risks;
- sensitive information in logs, analytics, notifications and error reports;
- consent, privacy notices and data handling where applicable;
- support process for account, access or data issues.
The NCSC advises organisations to use secure development practices across the delivery lifecycle. See NCSC secure development guidance.
For higher-risk mobile products, OWASP’s Mobile Application Security Testing Guide can help teams structure a proportionate security-testing approach. See OWASP MASTG.
Make analytics useful for launch decisions
Analytics should answer practical questions:
- Are users reaching the intended first-value moment?
- Where do they abandon a critical journey?
- Are users encountering repeated errors?
- Are important features being used as expected?
- Which cohorts or devices have more failures?
- Can support reports be connected to a product event or release?
Do not add tracking simply because it is available. Record only events needed to make a product, quality or support decision, and ensure analytics choices align with the product’s privacy approach.
Plan release, monitoring and rollback
A launch plan must explain what happens after the release button is pressed.
Assign owners for:
- release approval;
- production monitoring;
- customer support;
- incident decisions;
- communication with users or stakeholders;
- rollback or feature disablement;
- follow-up fixes and review.
Before launch, confirm:
- monitoring and error reporting work in production;
- alerts reach someone able to act;
- the team knows how to roll back or pause risky functionality;
- backups and restoration expectations have been tested where applicable;
- customer-support contacts and escalation routes are ready;
- release notes, store metadata and public information are accurate.
A practical go/no-go checklist
Use this checklist before launch.
| Area | Go/no-go question |
|---|
| Core journeys | Can intended users complete the important actions reliably? |
| Failure states | Are likely errors understandable and recoverable? |
| Data and permissions | Are records correct, private and accessible only to authorised roles? |
| Integrations | Are external services tested in the correct environment with clear failure handling? |
| Devices and networks | Has the supported test matrix been completed? |
| Accessibility | Have critical journeys been tested with relevant settings and assistive technology? |
| Security and privacy | Have high-risk controls, data flows and secrets been reviewed? |
| Analytics and monitoring | Can the team identify major failures and user friction after launch? |
| Support | Do users and internal teams know how to request help or escalate an issue? |
| Rollback | Can the team reduce harm if a serious issue appears? |
A “no” does not always mean cancel the launch. It means make an explicit decision: fix, reduce scope, limit the release cohort, add monitoring or accept a documented risk.
Conclusion
Good startup QA is not about chasing perfect test coverage. It is about building enough confidence in the outcomes that matter most and preparing for the failures that still occur.
Test the core journey, integrations, data, accessibility, security, analytics and rollback plan. Make ownership clear. Then launch with evidence, not hope.
Sources and further reading


 Mubeen AhmadCo-Founder24 Oct 20267 min read00