Winning interest from a large organisation is not the same as being ready to deliver. Enterprise partnerships can involve evidence, integration, security review, contracting, implementation, reporting and support beyond the sales conversation.
Readiness therefore has two distinct sides:
- Sales readiness: the company can explain the use case, value, commercial model and why the partnership is worth exploring.
- Operational readiness: the company can satisfy proportionate due diligence, contract responsibly, implement safely, support the service and govern the relationship after signature.
A technology business needs both. A strong pitch may open the door; evidence and delivery discipline determine whether the partnership can move through procurement and sustainable operation.
This guide is intended for UK technology founders and partnership leaders. It is an operational framework, not legal, regulatory, financial, insurance or compliance advice. Requirements vary by buyer, sector, data, access, service criticality and contract. Use advisers where appropriate.
Begin with the enterprise use case
Large organisations need a defined outcome that fits their priorities, constraints and accountability.
Before building an enterprise sales pack, answer:
- Which business unit or user owns the problem?
- What operational or commercial outcome matters?
- What happens today, and why is that inadequate?
- Who is the executive sponsor?
- Who owns the budget?
- Who will use, administer and support the product?
- What data or system access is required?
- How will value be measured?
- What would make the organisation stop the initiative?
The sponsor and buyer may not be the same person. Security, legal, procurement, finance, architecture, data protection, operations and users can each hold a different concern. Map them early.
Define the initial use case narrowly enough to evaluate. A bounded pilot may reduce uncertainty, but it should not defer every hard question. If the partnership could proceed to wider rollout, establish in advance what evidence the pilot must produce and what enterprise requirements a production service would need to meet.
Create a value case both parties can govern
Enterprise value should be expressed as an outcome, baseline and measurement method, not as a list of product features.
A useful value case includes:
- Baseline: the current process, cost, time, error, risk or experience.
- Target outcome: the change the partnership aims to create.
- Population: the teams, customers or transactions included.
- Evidence: the system or method that will measure progress.
- Dependencies: process, data, integration, training and adoption conditions.
- Review point: when both parties will decide whether to stop, adjust or expand.
Do not promise outcomes the product cannot control. If value depends on customer adoption, data quality or the buyer changing its process, state those dependencies. Separate a guaranteed deliverable from an intended business result.
Agree an executive owner on each side. Senior sponsorship helps resolve cross-functional obstacles, but operational owners still need authority for daily decisions.
Demonstrate product and service readiness
Enterprise buyers may evaluate not only what the software does today but how reliably the supplier can operate and change it.
Prepare a concise product-service overview covering:
- supported use cases and explicit exclusions;
- hosting and high-level architecture;
- relevant integrations and interface ownership;
- identity, access and administrator controls;
- availability targets and planned maintenance;
- backup, recovery and continuity approach;
- monitoring and incident handling;
- support channels, hours and severity definitions;
- product roadmap and change communication;
- accessibility and supported environments where relevant; and
- product retirement, data export and transition arrangements.
Be precise about current capability versus planned work. If an enterprise requirement needs custom development, clarify discovery, acceptance, ownership, support and commercial implications.
Know the integration boundary
For every integration, identify:
- which party provides and operates each endpoint;
- authentication and authorisation method;
- data fields, direction and frequency;
- rate, volume and latency expectations;
- validation and error ownership;
- monitoring and support responsibilities;
- versioning and change notice;
- test environments and test data; and
- fallback or continuity when the connection fails.
An architecture diagram should be understandable to reviewers without exposing unnecessary sensitive detail. Keep a more detailed controlled record for implementation and security review.
Set realistic service boundaries
An early-stage supplier should not promise support it cannot staff. Define response targets that match actual coverage, distinguish response from resolution and document critical escalation.
Prepare proportionate security evidence
Security review should reflect the access, data sensitivity, dependency and impact involved. A marketing questionnaire filled with “yes” answers is not strong evidence.
Start with a risk-based security pack:
- security roles and named accountability;
- secure-development practices;
- architecture and data-flow diagrams;
- asset, dependency and vulnerability management;
- access-control and privileged-access approach;
- encryption and key-management responsibilities;
- logging, monitoring and retention;
- backup and recovery testing;
- incident-response process and contact route;
- security testing and remediation process;
- supplier and subprocessor management;
- employee onboarding and offboarding controls;
- relevant certifications, with scope and expiry clear; and
- open risks, exceptions and planned improvements.
The National Cyber Security Centre’s Software Security Code of Practice implementation guidance is intended to help software vendors demonstrate how security is built into their products. Its themes include organisational accountability, secure design and development, deployment, communication and maintenance. Use it as a source of practices and evidence, not as a claim of certification unless a valid assurance scheme explicitly supports that claim.
The NCSC’s supply-chain principles advise organisations to understand suppliers and risk, communicate minimum requirements, build security into contracting, check arrangements and improve continuously (NCSC supply-chain principles). A supplier preparing for enterprise partnerships should expect the buyer to ask these questions and should apply similar discipline to its own critical providers.
Cyber Essentials can provide useful baseline assurance against common attacks, but no certification answers every risk. Explain scope, supporting controls and any additional measures needed for the use case rather than treating one badge as the entire security case.
Never send penetration-test reports, infrastructure details, credentials or other sensitive evidence through an uncontrolled sales process. Use access controls, confidentiality arrangements and a clear evidence owner.
Make privacy and data responsibilities explicit
Map the proposed processing before contract negotiation becomes urgent:
- What personal data is involved?
- Why is it necessary?
- Which party determines the purposes and means?
- Does either party act as a processor for the other?
- Which subprocessors are used?
- Where is data stored or accessed?
- How long is it retained?
- How are data-subject requests supported?
- What happens at contract end?
- How quickly must incidents be communicated?
The Information Commissioner’s Office states that when a controller uses a processor, a written contract must set out responsibilities and liabilities and include specified terms, including appropriate security and assistance with individual rights (ICO accountability and governance guidance). The ICO’s detailed processor-contract guidance is currently under review following the Data (Use and Access) Act, so check its latest position and obtain advice for the actual arrangement (ICO contracts and liabilities guidance).
Prepare a current subprocessor list, retention schedule and deletion or return procedure. Ensure sales material, privacy notices, technical reality and contractual statements agree. If the product changes its data flow, do not leave the contract and documentation behind.
Strengthen commercial and corporate readiness
Procurement teams may assess whether the supplier is a legitimate, stable and insurable counterparty. Prepare accurate, controlled records such as:
- registered company details;
- ownership and group structure;
- statutory filings and relevant financial records;
- current insurance certificates and policy scope;
- material subcontractors;
- intellectual-property ownership and licences;
- standard terms and order documents;
- conflicts or dependencies material to delivery; and
- references that customers have authorised you to share.
Companies House offers free access to registered information, officers, filings and insolvency information (GOV.UK company-information service). Buyers may use public records, so reconcile inconsistencies before diligence begins.
Insurance requirements should be discussed with a qualified broker. Policy names and headline limits do not prove that a specific activity, territory, data incident or contractual liability is covered. Do not agree liability or indemnity language solely because a deal is strategically attractive; obtain legal and insurance advice.
Build a contract issue list before receiving the buyer’s paper
Know your position on:
- scope, assumptions and acceptance;
- charges, invoicing and tax;
- service levels and service credits;
- customer responsibilities and dependencies;
- change control;
- intellectual-property ownership and licences;
- confidentiality;
- data protection and security;
- audit and assurance;
- warranties and remedies;
- liability and indemnities;
- subcontracting and assignment;
- term, renewal and termination;
- transition assistance and data return or deletion; and
- governing law and dispute process.
Plan implementation before signature
A signed contract can expose a weak operating model immediately. Build a joint implementation plan while commercial discussions continue.
Include:
- accountable owners and working-level leads;
- scope, dependencies and assumptions;
- technical integration and security tasks;
- data preparation or migration;
- configuration and acceptance;
- user communication and training;
- pilot or phased-rollout approach;
- launch criteria and rollback;
- support handover;
- reporting cadence; and
- decisions requiring executive escalation.
Use a responsibility matrix for material activities. Avoid assigning every task jointly: shared accountability can mean no accountability. Each deliverable needs one clear owner, contributors, due date and evidence of completion.
If a pilot is used, define:
- the target cohort and duration;
- the baseline and success measures;
- excluded functions or data;
- support and incident process;
- commercial treatment;
- intellectual-property and data handling;
- stop conditions; and
- what evidence would justify rollout.
Do not let a “free pilot” become an undefined production service. A pilot consumes implementation and support capacity and should test a decision that matters.
Design governance for the relationship you want
Enterprise partnerships need a rhythm after launch. Set governance proportionate to the relationship:
- operational review for service, incidents and near-term delivery;
- product review for adoption, feedback, roadmap and change;
- commercial review for usage, charges, obligations and forecasts; and
- executive review for value, strategic risks and expansion decisions.
Agree a small set of measures connected to the value case. Include leading indicators such as onboarding completion or adoption alongside service measures and business outcomes. Define data sources and owners so reports do not become monthly debates over calculation.
Create an escalation path with severity, contacts, response expectations and decision rights. Test it before a crisis. The ICO’s breach guidance states that processor reporting requirements should be detailed in the contract; organisations should also record breaches and investigate causes (ICO personal data breach guide). An operational incident may have contractual, security, privacy and communications consequences, so the teams need one coordinated process.
Governance should also handle change. Clarify how new features, integrations, material subprocessors, security changes and pricing changes are communicated and approved.
Prepare for exit before the partnership begins
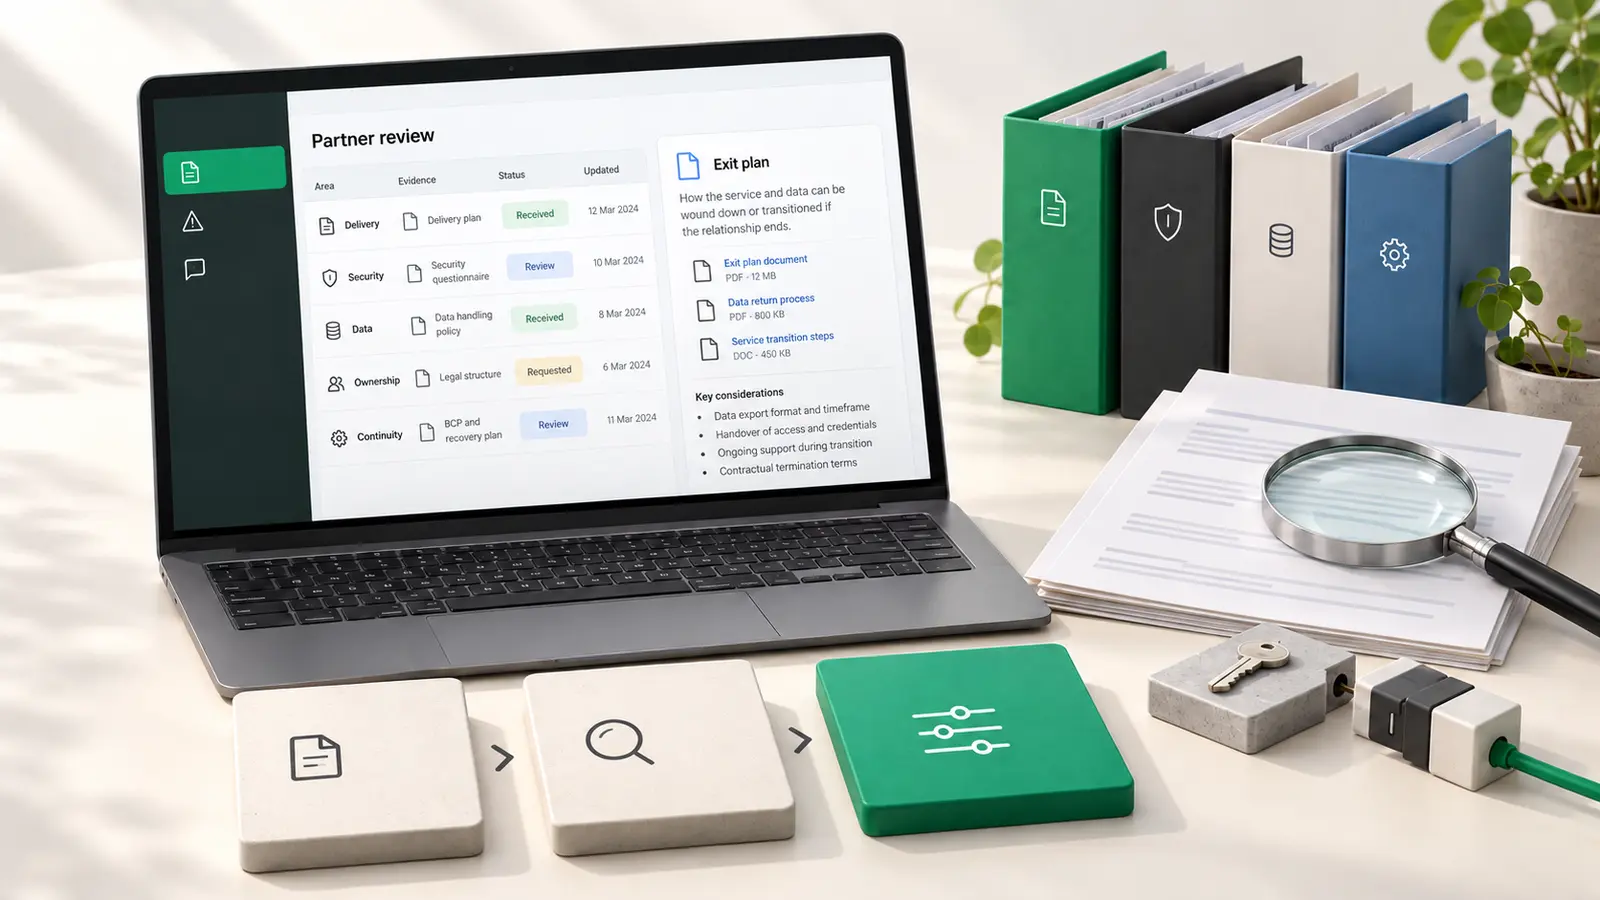
Exit planning signals maturity, not lack of confidence. The UK Government’s Digital, Data and Technology Playbook recommends planning early for expiry, extension, transition and termination, including knowledge transfer, support, asset and data transfer, responsibilities, milestones and dependencies. Its rules are written for central government and arm’s-length bodies, but the operational questions are useful for commercial partnerships too.
Agree:
- how customers export data in a usable format;
- deletion and confirmation arrangements;
- access removal;
- documentation and knowledge transfer;
- transition support and charges;
- treatment of customer-specific configuration;
- continuity during supplier distress or acquisition; and
- dependencies that could prevent an orderly move.
Strong exit terms can reduce perceived lock-in and make the initial commitment easier to approve.
Build a 30-day enterprise-readiness assessment
Before pursuing a material enterprise opportunity, run a focused assessment.
Week 1: Opportunity and stakeholders
- Define the use case, buyer, sponsor, users and value hypothesis.
- Map procurement, security, legal, architecture, privacy and operational stakeholders.
- Identify likely deal-breakers and decision dates.
Week 2: Product, data and security
- Review architecture, integrations, support and continuity.
- Map the data flow, roles, subprocessors and retention.
- Assemble current security evidence and record gaps honestly.
Week 3: Commercial and implementation
- Confirm pricing assumptions, delivery capacity and insurance questions.
- Prepare the contract issue list.
- Draft implementation, acceptance, governance and escalation plans.
Week 4: Evidence room and decision
- Organise approved evidence with access controls, owners and review dates.
- Run a cross-functional challenge session.
- Decide whether to proceed, narrow the scope, resolve priority gaps or decline.
An evidence room might contain company records, product and architecture summaries, security evidence, privacy documents, subprocessors, service model, insurance documents, implementation plan and standard terms. Every record should be current, relevant, approved to share and understood by an owner.
Classify gaps:
- Must resolve before progressing: a blocker to safe or lawful delivery.
- Resolve before contract: a material commitment requiring evidence or advice.
- Resolve before launch: an operational dependency with a clear owner and date.
- Improve during service: a controlled maturity improvement accepted by both parties.
This turns readiness into decisions rather than an endless compliance project.
Enterprise readiness is the ability to make credible commitments
A small technology business does not need to imitate the bureaucracy of a large buyer. It does need to know what it is promising and show how it will deliver.
The strongest enterprise-partnership position combines:
- a specific use case with an accountable sponsor;
- a measurable value hypothesis;
- clear product and integration boundaries;
- proportionate security and privacy evidence;
- commercially sustainable commitments;
- realistic implementation and support;
- governance that resolves problems; and
- an orderly exit path.
That foundation helps both sides evaluate the partnership honestly. It can shorten avoidable back-and-forth, surface unacceptable risk before commitment and preserve trust when delivery becomes complicated.
For wider partner selection context, read what UK buyers look for in a software development partner and build, buy or partner. If you want to assess a planned digital partnership, talk to FlutterCraft.
Sources and further reading


 Hassan KhanHead of Strategy & Partnerships24 Oct 202611 min read60